


How to Detect Shadow AI: Signals, Methods and a 30-Day Plan

Last updated: November 2026
To detect shadow AI, you need visibility at the device, where every AI request actually happens. Shadow AI detection is the process of finding the AI tools employees use without IT approval, then tying that use to real people, real accounts, and real data flows. Network logs tell you a domain was contacted. They don't tell you which AI tools your people rely on, how heavily, who's driving the usage, or whether the account is personal or enterprise. Here's how detection works, and a practical, step-by-step way to do it.
Key takeaways
- Shadow AI detection finds unsanctioned AI use and ties it to users, apps, accounts, and data.
- Four signals matter most: destination (which AI service), account type (personal vs. enterprise), process (browser vs. desktop app), and content (what's in the prompt or upload).
- Detection methods see different slices. On-device SSL inspection sees browsers and desktop apps, with content. DNS filtering sees domains. Cloud proxies see the web sessions steered through them. Browser extensions see the browser only.
- Start in visibility mode. Block personal accounts and add DLP once you've seen real usage.
- Good output isn't a raw log dump. It's a ranked view of top AI apps and top AI users that a CISO can read.
What signals reveal shadow AI use?
AI traffic leaves fingerprints. The trick is knowing which signals to read and where to read them. Four matter most.
- Destination. A connection to an AI service domain or model API endpoint tells you an AI tool is in play. It's the easiest signal to catch and the easiest to over-trust, because a domain alone doesn't tell you who, what, or how.
- Account type. A personal ChatGPT login and an enterprise ChatGPT login hit similar endpoints but carry very different risk. Enterprise accounts have data-handling agreements. Personal accounts don't. Telling them apart requires seeing inside the session, not just the domain.
- Process and device context. Traffic from a browser tab looks different from traffic generated by a desktop app or a command-line tool. Knowing which process made the request separates "someone opened a chatbot in Chrome" from "an AI CLI is running on this developer's machine." That context only exists on the endpoint.
- Content. The highest-stakes signal is what's in the prompt or the uploaded file: PII, PCI, PHI, source code, IP. Reading content requires decrypting the session and inspecting the payload, which is a much higher bar than logging a domain.
Catch only the destination and you get a list of domains. Catch all four and you get a story: this person, using this account, in this app, moved this data.
Which detection methods see shadow AI, and what does each miss?
There are six common places to look for AI traffic. Each sees a different slice, and the differences are the whole point.
| Detection method | What it sees | What it misses |
|---|---|---|
| On-device SSL inspection | Traffic per process and user, browser and desktop app, with content | Unmanaged devices without the agent. Sessions with certificate pinning need bypass handling |
| DNS filtering | AI service domains resolved by a device | Encrypted content, account type, process, in-app activity |
| Network or cloud proxy | Web sessions steered through the proxy | Off-path and off-network traffic, desktop apps not routed through it. Adds backhaul latency |
| Browser extensions | Browser-based AI use in detail | Anything outside the browser: desktop apps, IDEs, CLIs, scripts |
| CASB / SSPM (OAuth) | Third-party AI apps connected to your Microsoft 365 or Google tenant | Standalone chatbot use, prompts, and uploads outside the OAuth flow |
| DSPM | Sensitive data at rest in your repositories and cloud storage | Data in motion into AI tools. It doesn't observe prompts, so it can't see a paste into a personal AI account |
No single method is "wrong." They answer different questions. But if your goal is to see all shadow AI, the gaps in DNS-only and browser-only methods are the ones that hurt.
Why do DNS and browser-only tools miss shadow AI?
Two reasons: encryption and scope.
DNS filtering stops at the domain. It can tell you a device looked up an AI service, but the prompt, the account, and the uploaded file all sit inside a TLS session that DNS never opens. So DNS can flag that AI is happening. It can't tell you a personal account leaked source code. That's the difference between a smoke alarm and a camera. When Greylock Partners evaluated their old setup, DNS-only filtering was missing HTTPS traffic outright, which is one reason they moved off Cisco Umbrella to dope.security.
Browser extensions have the opposite problem. They see inside the browser in detail, but AI has moved out of the browser. ChatGPT Desktop, Claude Desktop, AI assistants baked into IDEs, and model calls fired from a terminal all run outside any browser tab. An extension can't see a single one of them. The same goes for MCP servers and IDE copilots wired to MCP, another surface that runs outside the browser.
That's why detection has to happen where the traffic originates. dope.SWG puts an on-device proxy on Mac and Windows endpoints and performs SSL inspection locally, so it isn't limited to the browser or to traffic that happens to be steered through a data center.
One honest caveat. On-device inspection only covers devices where the agent is installed, so unmanaged or BYO devices are out of scope, same as any endpoint-based method. Some apps also use certificate pinning, which can break inspection until an admin sets up a bypass. dope.security surfaces those SSL errors so admins can create bypasses in a few clicks, but it's a real step.
How to detect shadow AI, step by step
Step 1: Accept that it's already happening
Start from the assumption that employees are using AI, because they are. The goal isn't to catch wrongdoers. It's to get an accurate picture so you can make good policy. Framing it as discovery, not a witch hunt, gets you honest data.
Step 2: Measure at the endpoint, not the network
DNS and firewall logs undercount AI usage badly. They miss desktop apps like ChatGPT Desktop and Claude Desktop, they miss IDE assistants, and they can't distinguish a personal account from a corporate one.
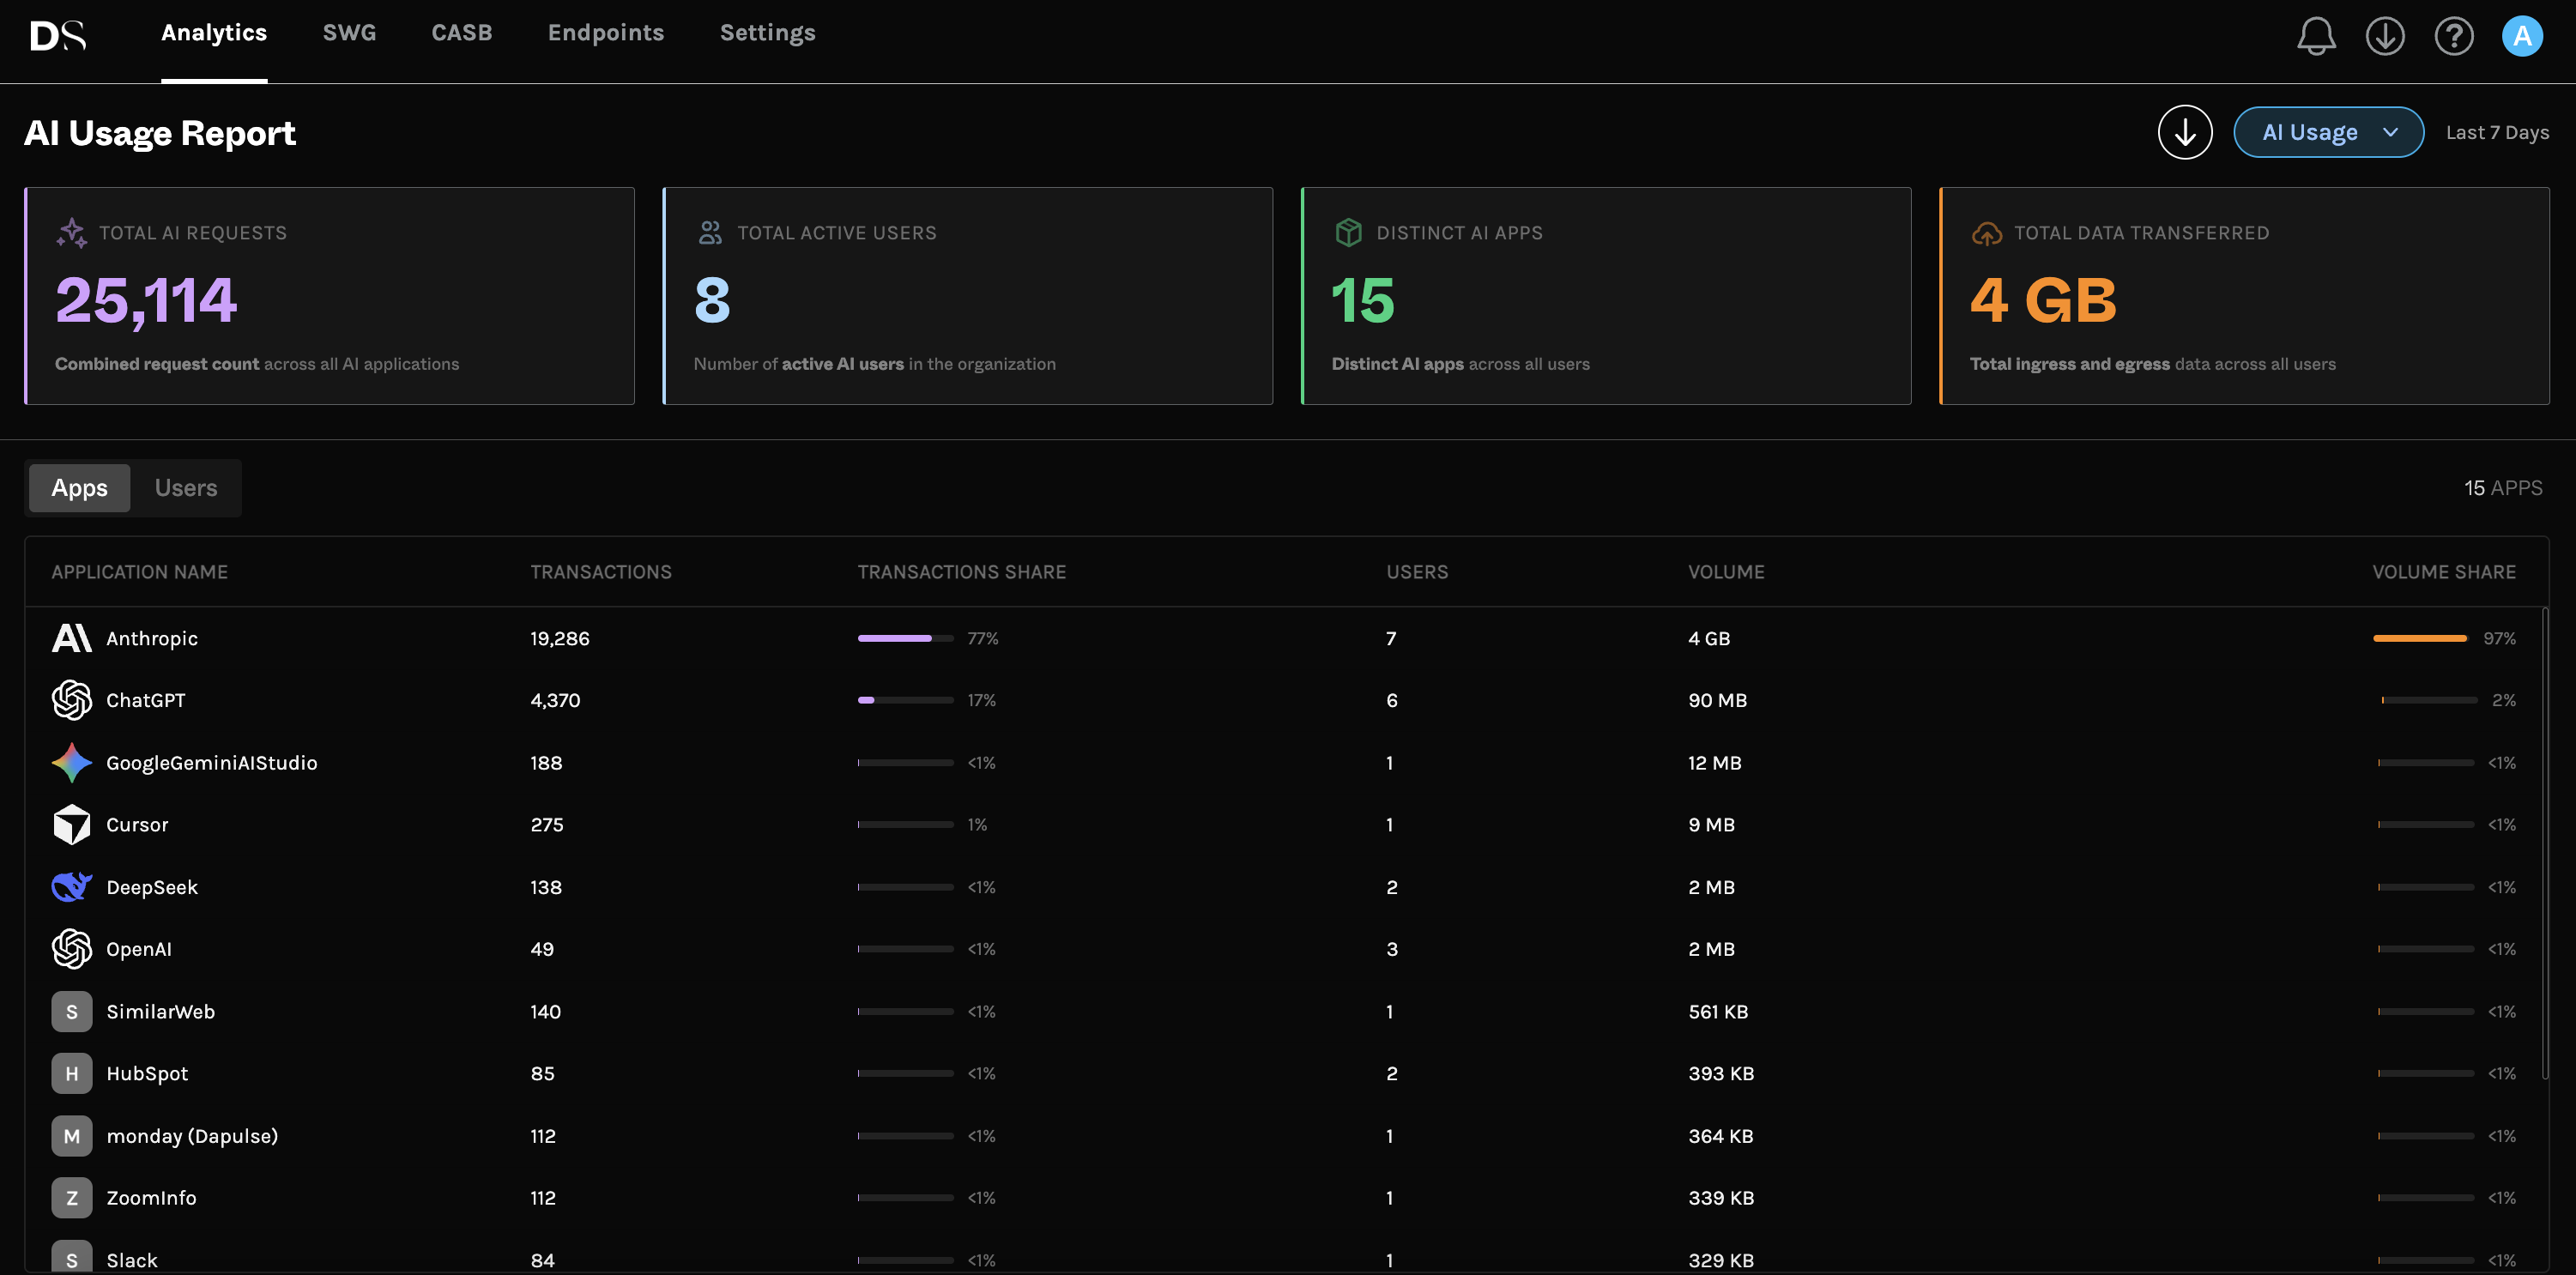
dope.security measures at the device. The dope.endpoint agent inspects traffic locally, so it captures AI requests across browsers and desktop apps, then feeds them into the AI Analytics view in dope.console.
Step 3: Read the four numbers that matter
The AI Analytics dashboard leads with the metrics you need for a first read on exposure:
- Total AI Requests across all AI applications.
- Active AI Users in the organization.
- Distinct AI Apps Detected across all users.
- Total Data Transferred, so you can see volume, not just hits.
All of it runs over a rolling 7-day window, so the picture stays current instead of going stale.
Step 4: Rank apps and users
Next, drill in. The view ranks the top AI applications by transactions and the top users by volume and by number of distinct apps, and shows whether each account is personal or enterprise-licensed. This is where patterns jump out: one team hammering a single tool, a handful of power users driving most of the traffic, or a long tail of niche apps you'd never have guessed.

If you'd rather ask than click, the Dopamine agent answers plain-language questions over the same data, like "Is anyone in the company using DeepSeek?" or "Users to investigate first," in under 10 seconds, and shows the steps it took.
Step 5: Turn the report into a conversation
dope.security includes an on-demand, branded PDF export of the AI usage report. Hand it to a CISO, an IT manager, or a compliance lead who doesn't live in the console. It turns "we think people use AI" into a document with numbers.
Step 6: Move from visibility to control
Detection is the start. Once you can see usage, layer on control: set secure web gateway policy to allow, warn, or block, use Cloud Application Control to permit enterprise tenants while blocking personal logins, and turn on Dopamine DLP to stop sensitive data from entering prompts and uploads in the first place. You can also block an app straight from the AI Usage screen, and the policy goes live on every endpoint.
Why not just block every AI tool?
Blanket blocking is the most expensive move available to you. People route around it: the work moves to a phone, a home laptop, or a tool you've never heard of. You lose the telemetry you need, because a blocked tool teaches you nothing. A domain block also can't tell your corporate workspace from a personal account on the same domain, so you block both or allow both. And it spends your credibility with employees. Here's how a blanket domain block compares with account-level control.
| Factor | Blanket domain block | Account-level control with on-device DLP |
|---|---|---|
| Detection after enforcement | Lost. Traffic goes to zero and you learn nothing | Preserved. All usage stays visible in analytics |
| Where usage goes | Personal phones, home laptops, unknown alternatives | Your enterprise tenant |
| Corporate versus personal accounts | Can't distinguish them. Same domain | Distinguished. Enterprise tenants allowed, personal logins blocked |
| Effect on productivity | Work stops or relocates | Work continues in a sanctioned workspace |
| Sensitive data protection | None once usage relocates | Sensitive data stopped at the prompt |
| Desktop apps, IDEs, CLI tools | Domain block may not apply at all | Covered by on-device inspection |
| Employee perception | Security says no | Security provided the licensed version |
| Time to change a decision | Change request, then propagation | Policy changes apply instantly |
What should a shadow AI detection program produce?
A shadow AI detection program should produce four outputs. If you can't produce all four, you have a feed, not a program.
- A named inventory of AI tools in use, with first-seen dates.
- Account attribution for each tool: personal login or enterprise tenant.
- User or team attribution, so you know whether it's three people or three hundred.
- Data-in-motion evidence: which categories of sensitive data actually moved, not just which sites people visited.
Volume alone is a vanity metric. "Two hundred ChatGPT sessions this week" tells you nothing. "Nine users on personal ChatGPT accounts, four of whom uploaded files containing PII" tells you what to do next.
What signs point to shadow AI before you have a tool?
If you're piecing it together before you have a proper tool, watch for:
- Traffic to AI domains from personal-looking sessions. Corporate SSO absent, personal accounts present.
- Desktop AI clients on managed devices. ChatGPT Desktop or Claude Desktop installed outside a sanctioned rollout.
- Spikes in outbound data to AI endpoints, which can indicate file uploads, not just chat.
- AI browser extensions requesting broad permissions.
- OAuth grants to AI note-takers and plugins in your Microsoft 365 or Google tenant.
- Expense reports for AI subscriptions IT never provisioned.
These are clues, not a system. They tell you shadow AI exists. They don't give you the who, what, and how much. For that you need continuous, device-level measurement. Our guide to the best shadow AI tools compares the options by where they sit.
A 30-day shadow AI detection plan
If you want a concrete rollout, this sequence works:
- Days 1 to 3: Deploy the dope.endpoint agent to a pilot group through your MDM and confirm the AI Analytics view is populating.
- Days 4 to 14: Observe in Monitor mode. Don't block anything yet. Let real usage surface.
- Days 15 to 21: Review the rankings. Identify sanctioned tools, risky tools, and personal-account usage worth converting to enterprise accounts.
- Days 22 to 30: Draft policy from the data, expand the rollout, and turn on enforcement where the risk is clear.
Don't block during the baseline period, because if you do, every number after that measures your enforcement, not your employees. Notice that detection and control blend together. The moment you can see usage, the fixes become obvious. For the data-protection layer, see our comparison of the top AI DLP tools. For what comes after detection, read shadow AI management best practices. New to the topic? Start with what shadow AI is.
How to detect shadow AI FAQ
What is shadow AI detection?
Shadow AI detection is the process of finding AI tools employees use without IT approval and attributing that use to specific users, apps, and data flows. It reveals who's using which AI tool, how much, and whether accounts are personal or enterprise.
What's the fastest way to detect shadow AI?
Deploy an on-device agent that reports AI usage automatically. With dope.security you can stand up the AI Analytics view quickly and see real data over a rolling 7-day window.
Can I detect AI use on personal accounts?
Yes. Because dope.security inspects on the device, it sees the request regardless of which account the employee logged in with, and shows whether the account is personal or enterprise-licensed.
Can DNS or firewall logs detect shadow AI?
Only partially. They can show a domain was visited but miss desktop apps, IDE assistants, account type, and the content of prompts, so they undercount badly.
Can a CASB or DSPM detect shadow AI?
Only partly. A CASB API connector reports on SaaS apps you've already sanctioned and connected, so it can't see an unsanctioned AI tool, a desktop app, or a CLI tool. DSPM finds sensitive data at rest and doesn't observe prompts in motion. Use a CASB to govern approved apps, not to discover unapproved ones.
Can shadow AI detection see desktop apps like ChatGPT Desktop or Claude Desktop?
Browser extensions can't, because those apps run outside the browser. On-device inspection can, because it watches traffic on the endpoint, covering browsers and desktop apps.
Is shadow AI detection the same as blocking AI?
No. Detection is visibility: knowing what's happening. Blocking is enforcement. You detect first, then decide policy.
How often should I review AI usage?
Treat it as continuous. A rolling 7-day view plus a periodic PDF export for stakeholders keeps the picture current as new tools appear.
Should I tell employees you're monitoring AI use?
Yes. Announce what you monitor and why before you turn it on. Transparency costs nothing in detection quality, because the goal is an accurate inventory, not a sting operation. It also buys you cooperation later, when you introduce account restrictions and DLP.
Ready to see your numbers? Manage AI with dope.security or book a 20-minute demo.


