


Best DLP Tools in 2026: 12 Data Loss Prevention Tools Compared
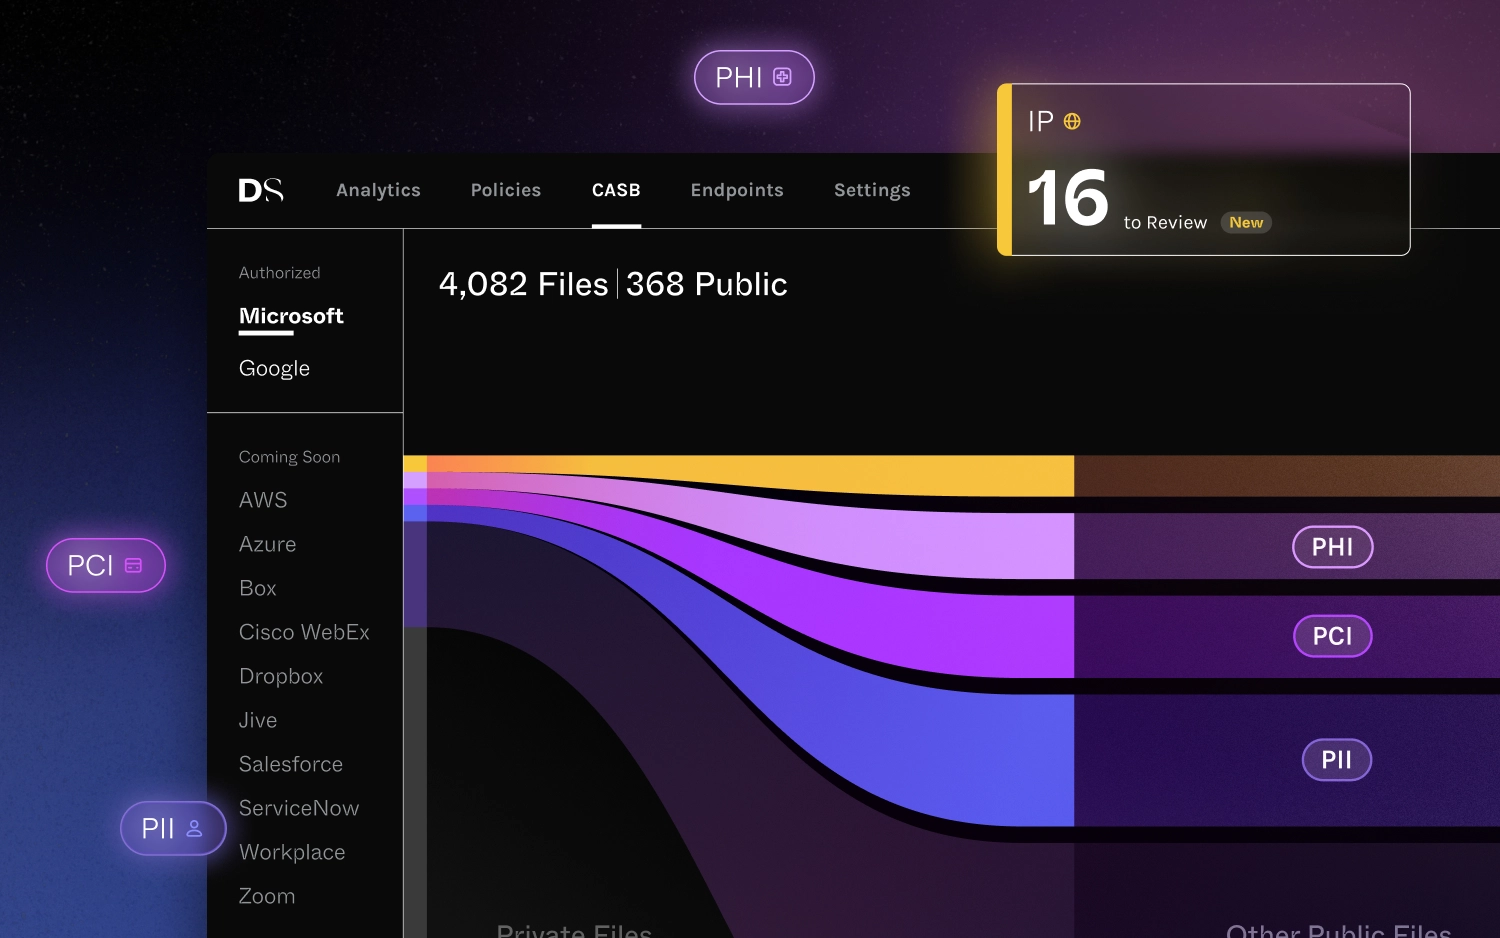
The best DLP tool is the one standing where your data actually leaves. In 2026, that's usually not an email attachment. It's a paragraph pasted into ChatGPT on a laptop at home.
Most DLP tools inspect in one of two places: inside a SaaS tenant after the file has landed, or in a cloud proxy after traffic has detoured to a data center. Below are 12 DLP tools compared on the question that separates them: where does inspection happen, and is your user already past it?
Quick picks
- Best for laptops, AI prompts, and remote teams: dope.security (Dopamine DLP + CASB Neural)
- Best if you live in Microsoft 365: Microsoft Purview
- Best for CASB-led SaaS control: Netskope
- Best for large global SSE rollouts: Zscaler
- Best for mature, policy-heavy DLP programs: Forcepoint
- Best for email-first data loss: Proofpoint
- Best API-only DLP for SaaS apps: Nightfall
DLP tools compared
| Tool | How it's delivered | Where it inspects | AI prompt coverage | Best for |
|---|---|---|---|---|
| dope.security | Endpoint agent + API (cloud DLP) | Intercepted on the device; only extracted text is classified | Included (Dopamine DLP + AI Analytics) | Hybrid/remote teams, AI governance |
| Microsoft Purview | Native to Microsoft 365 + Windows/macOS endpoint | In the M365 tenant and onboarded devices | Strongest inside Microsoft Copilot | Microsoft-standardized orgs |
| Netskope | Cloud proxy (SSE) + API CASB | Netskope NewEdge PoP | AI Guardrails, higher tier | CASB-heavy SaaS control |
| Zscaler | Cloud proxy (SSE) | Zscaler service edge | Data Protection add-on | Global enterprise SSE |
| Forcepoint | Cloud proxy + endpoint | Forcepoint cloud / endpoint | GenAI Security, multi-SKU | Policy-heavy DLP programs |
| Palo Alto Prisma SASE | Cloud proxy (SASE) | Prisma Access PoP | AI Access Security add-on | Palo Alto firewall estates |
| Symantec (Broadcom) | On-prem + endpoint + cloud | Network, endpoint, cloud | Limited, no tenant control | Large legacy estates |
| Proofpoint | Email + endpoint + cloud | Mail flow, endpoint | Varies by module | Email-first data loss |
| Nightfall | API (SaaS) + browser | Inside connected SaaS apps | Browser-based for GenAI | SaaS-only DLP |
| Cloudflare One | Cloud edge proxy | Cloudflare edge | AI Prompt Protection (beta) | Edge-first, developer-led teams |
| Cisco Umbrella | DNS + cloud SWG add-on | Cisco SIG (with SWG) | Response DLP, ChatGPT only | Cisco-standardized shops |
| Fortinet FortiSASE | Firewall + cloud SASE | FortiGate / FortiSASE PoP | Pattern-based | Fortinet firewall estates |
Delivery is the column that decides everything else. The rest of this guide explains why.
1. dope.security: Dopamine DLP + CASB Neural
Best for: hybrid and remote teams that need to stop data going into AI tools without banning them.
dope.security moved the secure web gateway off the stopover data center and onto the endpoint, then built DLP into it. Endpoint DLP, cloud DLP, SaaS posture, and AI analytics all live in one console.
- Data in motion: Dopamine DLP. Watches file uploads and AI prompts on the endpoint. Text is extracted on the device, and only that text (never the original file) goes to a private LLM for a Sensitive or Not Sensitive verdict. No data retention, no training on your data. It reads meaning instead of matching regex, detects PII, PCI, PHI, and intellectual property, and needs zero policy configuration to deliver value on day one.
- Enforcement that fits the business. Run each policy in Block, Monitor, or Off, then carve out exceptions by user or group (say, a finance team that handles PCI data). Every violation comes with a Dopamine Summary, a plain-language explanation of what was caught and why. US Patent 12,464,023.
- Data at rest: CASB Neural. One-click activation across Google Workspace and Microsoft 365, no connectors, no rules to write. It finds every externally shared Drive and OneDrive file, gives an LLM-written summary of what makes it sensitive, and makes it private again in one click.
- SaaS posture: SSPM. Inventories every third-party app authorized on your tenant, with scope, risk rating, consent type, permissions, and sign-ins.
- AI visibility and account control. AI Analytics shows ChatGPT, Claude, Gemini, Copilot, and shadow AI by user, split by personal versus enterprise-licensed accounts. Cloud Application Control allows the enterprise tenant and blocks the personal account, including in the Claude desktop app. Ask the Dopamine agent "is anyone using DeepSeek?" and get an answer in seconds.
- Which app sent it. Because inspection runs at the endpoint's networking layer, telemetry can record the originating process, so you can tell Chrome from the ChatGPT desktop app from a Python script hitting the same AI service.
The catch: dope.security is an endpoint-first SWG plus DLP for Mac and Windows, not a decades-old enterprise DLP suite with on-prem database discovery. If you need to scan file servers in a data center, pair it with a data-at-rest tool for those.
Proof: Outreach Health secured 99% of devices in a week. A Fortune 100 customer scaled from 900 to 18,000+ devices in weeks. SOC 2 Type 2 and GDPR compliant.
2. Microsoft Purview
Best for: organizations already standardized on Microsoft 365 E5.
Purview applies sensitivity labels and DLP policies across Exchange, SharePoint, OneDrive, Teams, and onboarded Windows and macOS devices. If your data lives in Microsoft, it's the tool you may already be paying for.
AI prompt coverage: strongest for Microsoft Copilot. Coverage of third-party AI tools depends on endpoint DLP and browser setup.
The catch: Purview's view is shaped like your tenant. Once a file leaves for a personal account or a non-Microsoft AI tool, coverage gets thin, and policy tuning across labels and locations is real work. Our Purview DLP alternative guide covers the gap.
3. Netskope
Best for: CASB-heavy buyers who want deep SaaS control.
Netskope's DLP sits inside its SSE platform and is strong on SaaS app visibility, separating managed and unmanaged app instances. AI Guardrails, shipped in April 2026, inspects prompts and responses in real time.
The catch: inspection runs through the NewEdge proxy network. Netskope's SLA allows under 10 ms of added latency for non-decrypted traffic and 50 ms for decrypted traffic, which is exactly the traffic DLP has to read. Full inline DLP and AI controls sit in the higher Max Advantage tier, and the API CASB is a separate SKU.
4. Zscaler
Best for: large global enterprises standardizing on one SSE vendor.
Zscaler inspects all traffic inline in its Zero Trust Exchange and lets admins tune DLP down to the individual user.
The catch: every request forwards to a Zscaler service edge first, and Gartner has cited a 10 to 20% throughput drop as inspection modules stack. Prompt-level DLP needs the Data Protection add-on, with AI Guard and AI Scanning licensed separately. Cert-pinned apps and developer tools such as Docker, Python, and Git commonly end up on bypass lists.
5. Forcepoint
Best for: mature DLP programs with dedicated policy staff.
Forcepoint has some of the deepest policy controls and compliance reporting in the category, across web, cloud, email, and endpoint.
The catch: setup and tuning are heavy. Cloud traffic backhauls through roughly 300 AWS points of presence, customers report policy changes taking 20 to 30 minutes to take effect, and GenAI Security is a multi-SKU assembly. Forcepoint's own knowledge base confirms its service is blocked in China.
6. Palo Alto Prisma SASE
Best for: teams committed to Palo Alto firewalls.
Enterprise DLP runs across Prisma Access, SaaS Security, and NGFWs with a consistent policy engine and behavior analytics.
The catch: AI Access Security stacks on top of Enterprise DLP as a separate license, and inline AI inspection runs through the decrypt proxy. Setup complexity is the most cited complaint, and the GlobalProtect agent has vendor-confirmed macOS battery and CPU issues.
7. Symantec DLP (Broadcom)
Best for: large estates that already run it and have the staff to maintain it.
Symantec covers endpoint, network, storage, and cloud with deep regulatory templates.
The catch: its documented GenAI capability dates to April 2023 and has no corporate-versus-personal tenant control. Renewal economics are the most-cited pain under Broadcom, with mid-market renewals reported at two to four times prior pricing. See our Symantec WSS alternatives guide.
8. Proofpoint
Best for: organizations where email is the main way data leaves.
Proofpoint pairs email DLP with endpoint and cloud coverage plus user behavior analytics to flag risky insiders.
The catch: it's strongest in the inbox. Web uploads and AI prompts depend on which modules you license, and it's priced as an enterprise product.
9. Nightfall
Best for: SaaS-first teams that want API-based DLP without an agent or proxy.
Nightfall connects to apps like Slack, Google Drive, and GitHub through their APIs and uses ML detectors to find secrets and sensitive data at rest.
The catch: API-based DLP sees what lands in a connected app, not what leaves a laptop. A personal ChatGPT session or a desktop AI client is outside its view unless you add browser coverage.
10. Cloudflare One
Best for: edge-first, developer-led teams already on Cloudflare.
DLP runs on Cloudflare's global edge alongside its SWG and ZTNA.
The catch: full DLP, unlimited CASB, and remote browser isolation sit in the Contract plan (see Cloudflare Zero Trust pricing). AI Prompt Protection launched in beta in August 2025 for about four apps, and TLS inspection commonly breaks git, kubectl, Docker, and the ChatGPT desktop app.
11. Cisco Umbrella
Best for: Cisco-standardized shops.
Umbrella DLP adds PII, PCI, and PHI policies plus prebuilt regulatory templates on top of Cisco's SIG.
The catch: DNS-layer Umbrella can't read URLs or payloads. Cisco doc 225162 says allowing a corporate ChatGPT instance while blocking personal ones needs the intelligent proxy, SSL decryption, and a root certificate. Response DLP is documented for ChatGPT only. See Cisco Umbrella DLP in 2026.
12. Fortinet FortiSASE
Best for: Fortinet firewall estates.
DLP runs on FortiGate firewalls and FortiSASE with FortiGuard updates and tight fabric integration.
The catch: classification leans on pattern and keyword matching rather than content understanding, and full coverage across email, web, and endpoint means buying more Fortinet products.
How to choose a DLP tool
Feature lists converge. Architecture doesn't. Ask every vendor these four questions:
- Where does inspection happen? In a SaaS tenant (API), in a cloud proxy (after a detour), or on the device (before data leaves)? Most organizations need the first and the third.
- Does it understand content or match patterns? Regex and dictionaries flood your queue with false positives on unstructured text like strategy notes and source code.
- Can it tell a corporate account from a personal one on the same domain? If the answer involves a proxy, a data protection module, and a higher tier, write that into the cost.
- What does it see outside the browser? Desktop AI apps, IDEs, and command-line tools never touch a browser extension. An endpoint agent that inspects locally sees them and can tell you which process sent the data.
[EMBED: Fly-Direct Speed Test. Add the Embed block here (copy it from the SWG post) or delete this line before publishing.]
Every DLP tool that inspects in a cloud point of presence adds a round trip to every request: roughly 40 to 80 ms near a PoP, 150 to 400 ms far from one. See what that detour costs on your own connection.
Want more depth? Our cloud DLP buyer's guide covers evaluation criteria, endpoint DLP vs network DLP covers the inspection question, and the best AI DLP tools narrows the list to tools that actually inspect prompts.
Frequently asked questions
What is a DLP tool?
Data loss prevention (DLP) tools find sensitive data like PII, PCI, PHI, and intellectual property, and stop it from leaving your control. They cover data in motion (uploads, web, email), data at rest (cloud storage, file shares), and data in use (copy, paste, USB).
What is the best DLP tool in 2026?
It depends on where your data leaves. For files in sanctioned SaaS, an API tool like Microsoft Purview or Nightfall can be enough. For text going into AI tools from laptops, you need inspection on the endpoint. dope.security covers both: Dopamine DLP for data in motion and CASB Neural for data at rest.
What is the difference between endpoint DLP and network DLP?
Network DLP inspects at a gateway or cloud proxy, after data has already left the device. Endpoint DLP inspects on the device first, so it also sees desktop apps, IDEs, and command-line tools.
Do DLP tools work on AI prompts?
Some do, and most charge extra. Zscaler puts prompt DLP behind its Data Protection add-on, Netskope puts AI Guardrails in its top tier, and Cloudflare's AI Prompt Protection is a beta. Dopamine DLP includes prompt and upload inspection as part of dope.security.
Can DLP block personal ChatGPT but allow the corporate account?
Only if it can read the tenant inside decrypted traffic on the same domain. DNS-only tools can't. dope.security does it on the device with Cloud Application Control: enter your ChatGPT workspace ID or Claude org ID, and personal free and paid accounts are blocked while the enterprise tenant keeps working, on any network.
Is Microsoft Purview enough on its own?
Inside Microsoft 365, often yes. Once data heads to a personal account or a non-Microsoft AI tool, you need egress inspection that doesn't depend on the destination being your tenant.
How long does DLP take to deploy?
Legacy enterprise DLP is often measured in months. On-device DLP skips traffic steering: dope.security customers deploy through existing MDM in days, like Outreach Health at 99% of devices in one week.
Does on-device DLP send my files to the cloud?
Not with dope.security. Dopamine DLP extracts text on the device and sends only that text for classification, never the original file, with no retention and no training on your data. SSL decryption itself never leaves the laptop.
Try it
See which files in your organization are already exposed and what's flowing into AI tools right now. Try dope.security free, or book a 20-minute demo.


